Article
Cybersecurity
CISO-as-a-service consulting: posture, remediation roadmap, ongoing support.
Discover →
CyberAgent
Continuous vulnerability assessment and gap analysis: scanning, mapping onto framework requirements, documentary evidence ready to use.
Discover CyberAgent →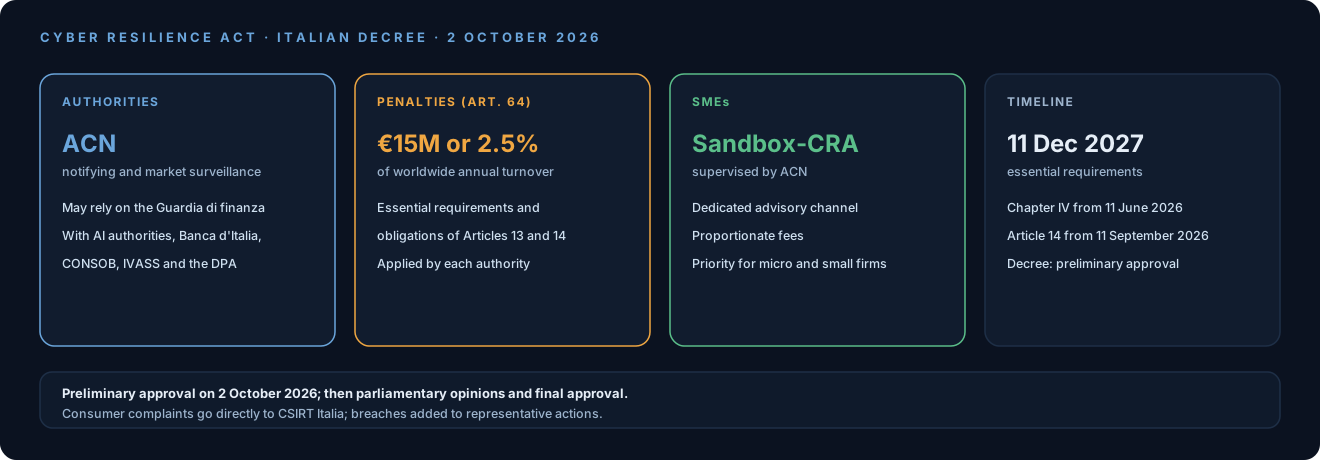
On 2 October the Italian Council of Ministers gave preliminary approval to the legislative decree adapting national law to Regulation (EU) 2024/2847, the Cyber Resilience Act. The text was proposed by the Prime Minister and the Minister for European Affairs, the NRRP and Cohesion Policies. The delegation is in Article 15 of Law no. 36 of 17 March 2026, the 2025 European Delegation Law.
The regulation applies directly. The decree sets out who supervises in Italy, how penalties are applied and which tools the smallest companies get.
Who supervises
The National Cybersecurity Agency (ACN) has two roles:
- notifying authority for conformity assessment bodies, which are assessed and monitored by the national accreditation body;
- market surveillance authority, with the option of relying on the Guardia di finanza.
Other authorities supervise in their own areas:
- for products that are also high-risk AI systems, the authorities competent under the national AI rules;
- for supervised financial institutions, Banca d’Italia, CONSOB and IVASS;
- for matters within its remit, the Italian data protection authority (Garante per la protezione dei dati personali).
The authorities work in coordination, including through information-sharing agreements.
Penalties and complaints
Each authority applies the regulation’s administrative penalties under its own procedures. The maximum amounts are set by Article 64 of the regulation:
- up to €15 million or 2.5% of worldwide annual turnover, if higher, for the essential requirements of Annex I and the obligations of Articles 13 and 14;
- up to €10 million or 2% for the other obligations listed in paragraph 3, including those of importers and distributors;
- up to €5 million or 1% for incorrect, incomplete or misleading information supplied to notified bodies and market surveillance authorities.
Consumers can report vulnerabilities, incidents and cyber threats directly to CSIRT Italia. Breaches of the regulation are also added to the matters for which representative actions can be brought to protect consumers’ collective interests.
SMEs and the Sandbox-CRA
For the smallest companies the decree provides:
- a dedicated advisory channel for micro, small and medium-sized enterprises and start-ups, defined by ACN and the Ministry of Enterprises and Made in Italy;
- proportionate fees for conformity assessment;
- a regulatory sandbox, the Sandbox-CRA, supervised by ACN.
The dedicated channel and regulatory sandboxes are provided for in Article 33 of the regulation. The Sandbox-CRA offers controlled testing environments to develop and verify innovative products before they are placed on the market. Micro and small enterprises get priority access. The sandbox is coordinated with those for financial services and for artificial intelligence.
The timeline
Article 71 of the regulation sets three dates:
- from 11 June 2026 Chapter IV applies, on notifying authorities and notified bodies;
- from 11 September 2026 Article 14 applies, on reporting actively exploited vulnerabilities and severe incidents;
- from 11 December 2027 the rest of the regulation applies, including the essential cybersecurity requirements.
As of 3 October the first two dates have already passed. After the preliminary approval the draft goes through the required opinions, including those of the parliamentary committees, and then back to the Council of Ministers for final approval before publication in the Official Gazette.
What we think
The draft confirms ACN as the main point of reference for the cybersecurity of digital products, with the sector authorities for finance, personal data and AI. For a manufacturer it means knowing whom to answer to and with which tools, starting from the SME channel and the Sandbox-CRA. The operational details (penalty procedures, fee amounts, sandbox access rules) will require the text of the draft, which the press release does not include.
What to watch
- The publication of the draft as a government act and the opinions of the parliamentary committees.
- Final approval and publication in the Official Gazette.
- The penalty procedures of each authority and how they coordinate.
- The conformity assessment fees and the rules of the Sandbox-CRA.